Broken Access Control (A01) is ranked as the first category in the OWASP Top 10:2025 because it remains one of the most dangerous and commonly exploited web application vulnerabilities. It occurs when users…
Read more
Secure coding practices are a set of development techniques and security measures followed by software developers to minimize vulnerabilities during the software development lifecycle (SDLC). Security should be incorporated from the initial design…
Read more
Effective backend performance depends on a server environment that mirrors the asynchronous nature of the runtime. Node.js maintains peak efficiency through a non-blocking architecture that processes thousands of concurrent connections without draining system…
Read more
When visitors come to a basic WordPress hosting website, the site’s performance is a critical factor in their perception of the website. Fast page load times generally allow users to browse through content,…
Read more
With cyber threats increasing every year, the demand for skilled web application security engineers is growing rapidly. Organizations across industries need professionals who can secure websites, applications, APIs, and cloud systems from hackers…
Read more
Large Language Model (LLM) applications are becoming increasingly popular in modern web applications. However, insecure integration of APIs with LLMs can introduce critical vulnerabilities. One such issue is “excessive agency,” where an LLM…
Read more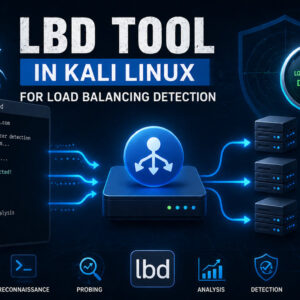
Load Balancing Detection (lbd) is a lightweight information gathering tool in Kali Linux used to identify whether a target domain is using load balancing mechanisms such as DNS-based or HTTP-based distribution. It is…
Read more
Artificial Intelligence is no longer a futuristic concept—it’s a daily productivity companion. From content creation and coding to video generation and research, AI tools are transforming how individuals and businesses operate. Whether you’re…
Read more
API security testing has become a critical part of modern web application assessments. Many organizations expose APIs without fully securing all endpoints, which can lead to serious vulnerabilities. In this hands-on guide, we’ll…
Read more
Vulnerability Assessment and Penetration Testing (VAPT) is a critical practice for securing modern web applications. With cyber threats constantly evolving, organizations must proactively identify and fix security weaknesses before attackers exploit them. A…
Read more